Built to pass your security review
VIREOPS runs in your own tenancy. Your estate data never leaves it, there is no vendor login, and every control below is enforced in the product and tested in every release.
Your data never leaves your tenancy
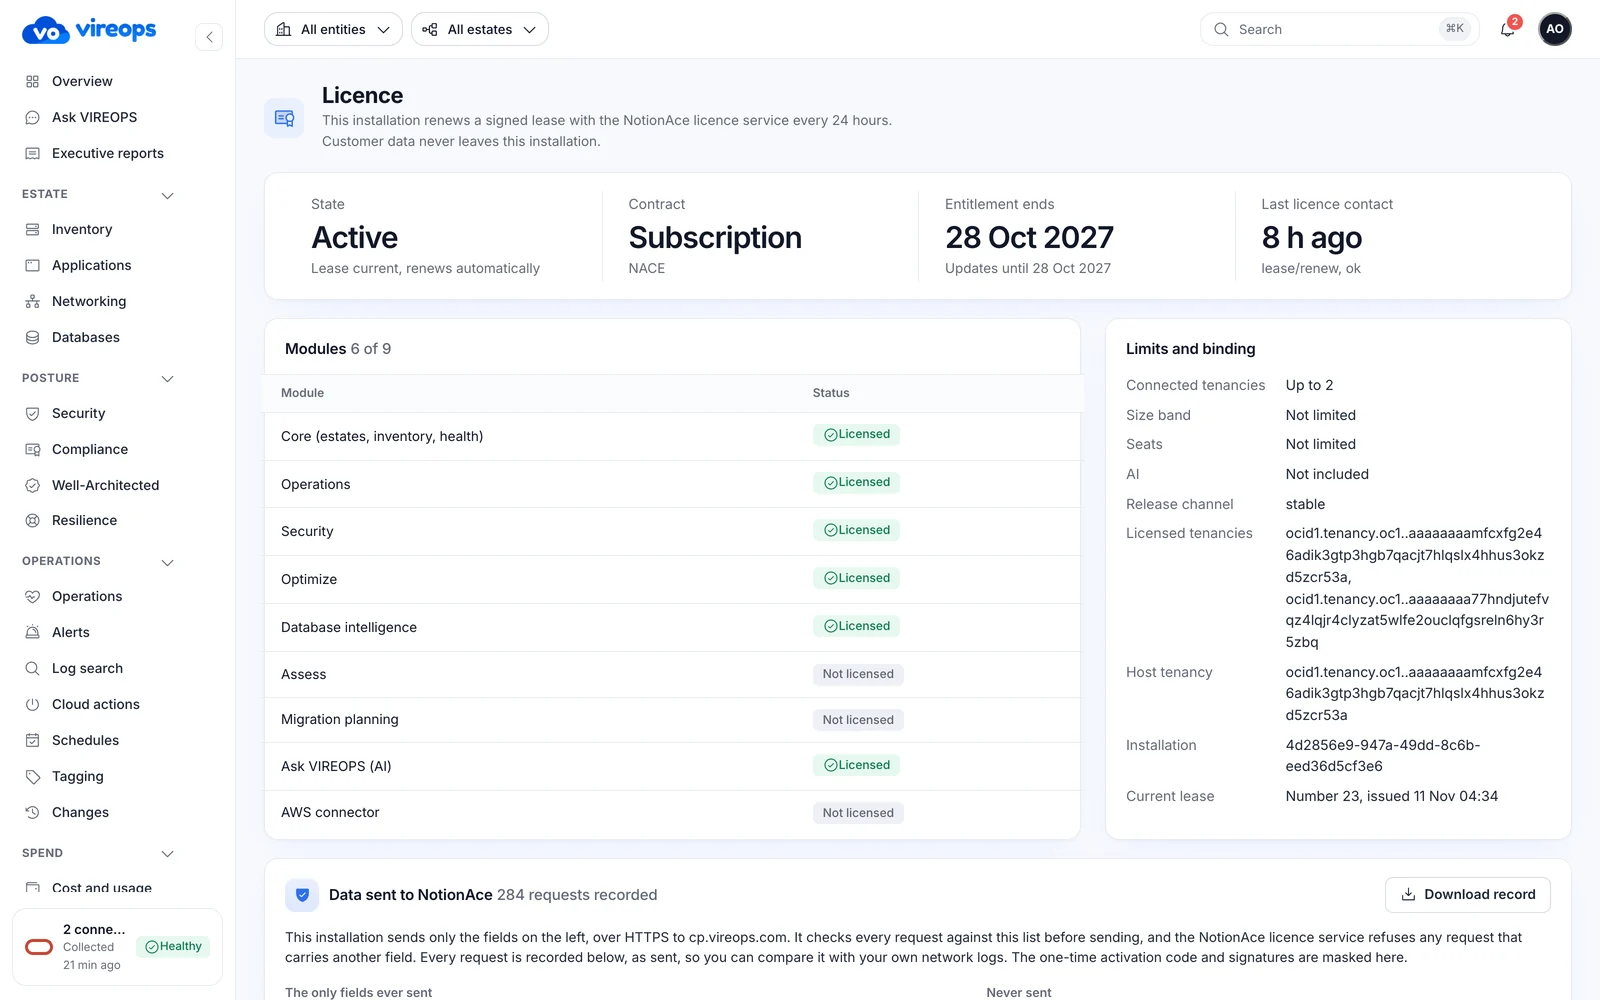
The install's only outbound connection to NotionAce is the licence agent calling the Control Plane over HTTPS. Every field it may carry is on one published list, and the list is code, enforced at both ends.
Sent to NotionAce
- A random installation ID, the public half of its signing key, and an Ed25519 signature on every request
- The host tenancy OCID the licence is bound to, with a short-lived signed proof
- Product version, platform and the VM's clock time
- Three counts: connected tenancies, billable resources and seats
Never sent
- Resource, compartment, database or network names, OCIDs other than the host tenancy, IP addresses
- Costs, usage, metrics, findings, compliance results or reports
- Cloud credentials, connection settings, AI provider keys or passwords
- User names or email addresses, Ask VIREOPS questions or answers
- Database contents of any kind
The product has no analytics, crash reporting or third-party tracking.
The install refuses
Each request is checked against the list before it is sent. A request with any other field is refused and never leaves the VM.
The Control Plane refuses
Any request carrying a field outside the list is rejected, including an unknown key inside the counts or the tenancy proof.
The build refuses
Tests fail CI if the agent sends, or the Control Plane accepts, anything outside the list. Every request body is also recorded in your own database.
| Other traffic from the install | What it is |
|---|---|
| NotionAce release registry | Signed images downloaded only when an update is installed, with a short-lived, pull-only token. Nothing is uploaded |
| OCI APIs | Read-only collection and opt-in operations, under your own policies |
| Your AI provider | Only when you add your own key |
| Your email service | Only if you configure one |
Isolation enforced by the database
VIREOPS is built multi-tenant from day one, so separation between accounts and entities is a database rule, not a convention in the code.
Row-level security
Forced on every owned table, every query. The runtime roles are never owner and never bypass RLS. SQL is parameterised only.
Encrypted secrets
AES-256-GCM, bound to the account and row. Secrets never appear in the repo, logs or the browser.
Entity separation
Subsidiary-level separation enforced by the database. Entity-scoped admins stay inside their entities.
Evidence you can trust
Evidence is stored immutably with a SHA-256. Nothing is hard-deleted: a deleted resource goes missing, then archived, and can be restored.
Keys stay home
Vendor signing keys stay in AWS KMS only. Installs embed only the public keys they need to verify releases and licences.
Retention
Metrics, changes and compliance runs are kept 400 days. Audit, evidence and cost are never deleted.
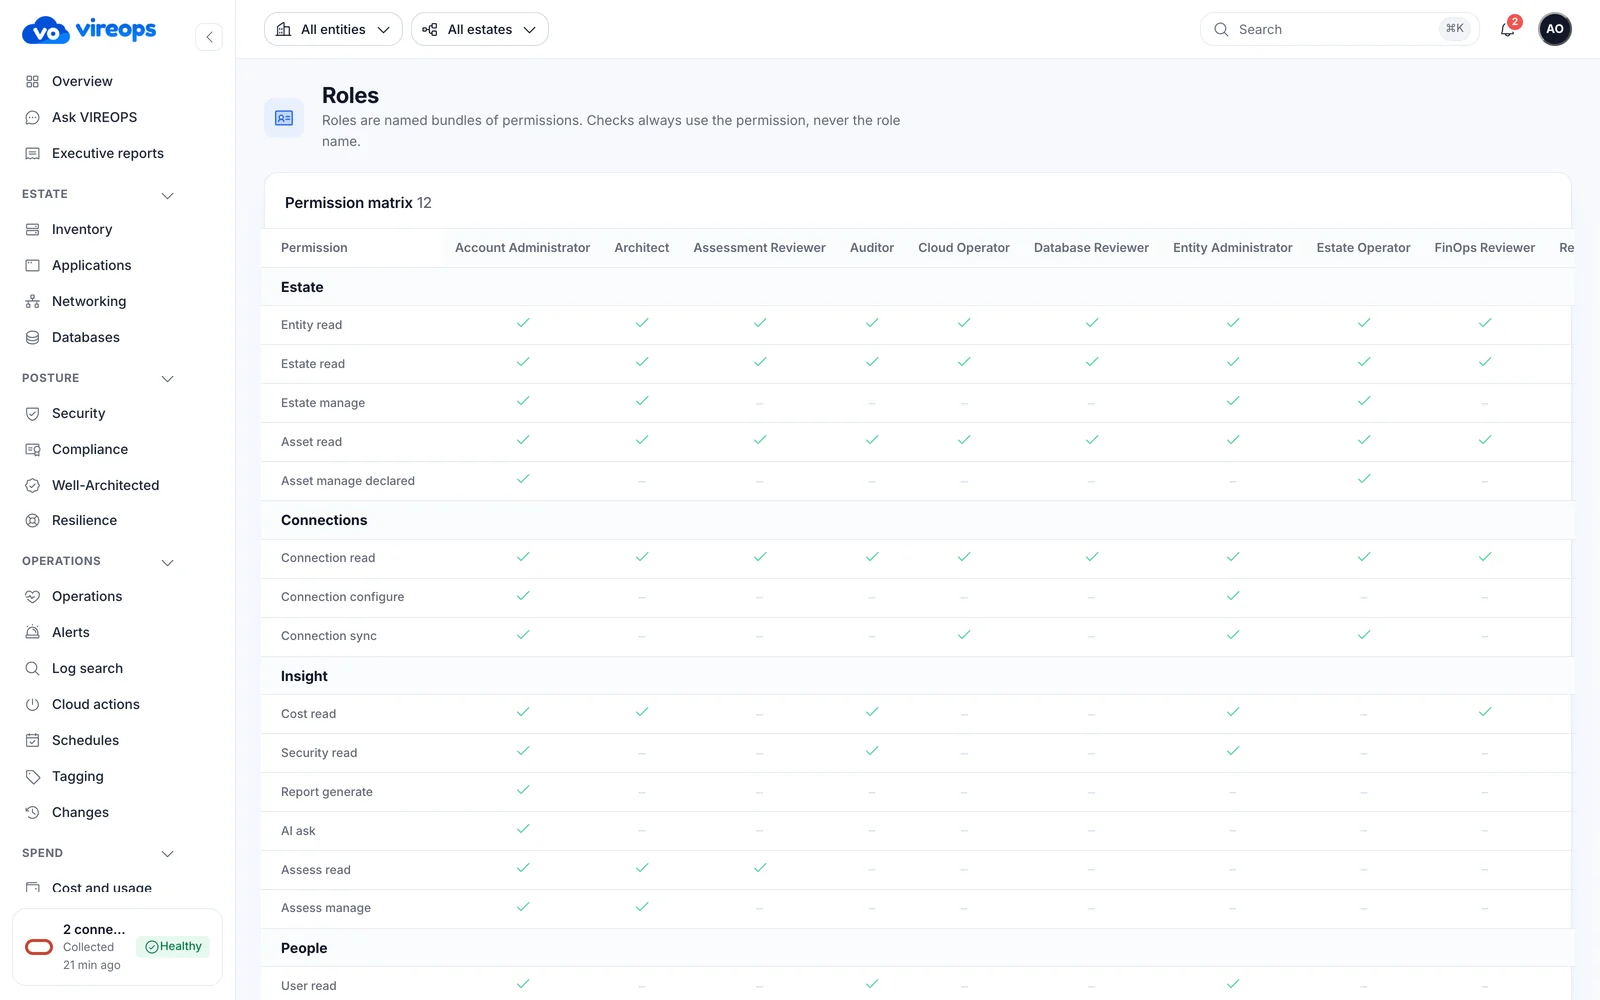
Sign-in, SSO and 12 built-in roles
Fine-grained, entity-scoped permissions. Nobody can grant a permission they don't hold.
- Passwords: Argon2id with a breached-password check, CSRF protection, and login backoff per account and per IP
- MFA: TOTP, mandatory for admin permissions, with recovery codes
- Sessions: time out after 60 minutes idle or 12 hours in total, and can be revoked under "Your sessions"
- OIDC single sign-on: PKCE, signatures checked against the provider's keys, group-to-role mapping, auto-provisioning. A user with no mapped role is refused
Not yet: SAML.
| Group | Built-in roles |
|---|---|
| Administration | System Administrator, Account Administrator, Entity Administrator |
| Operations | Cloud Operator, Estate Operator, Architect |
| Review | Security Reviewer, FinOps Reviewer, Database Reviewer, Assessment Reviewer |
| Read and audit | Auditor, Report Viewer |
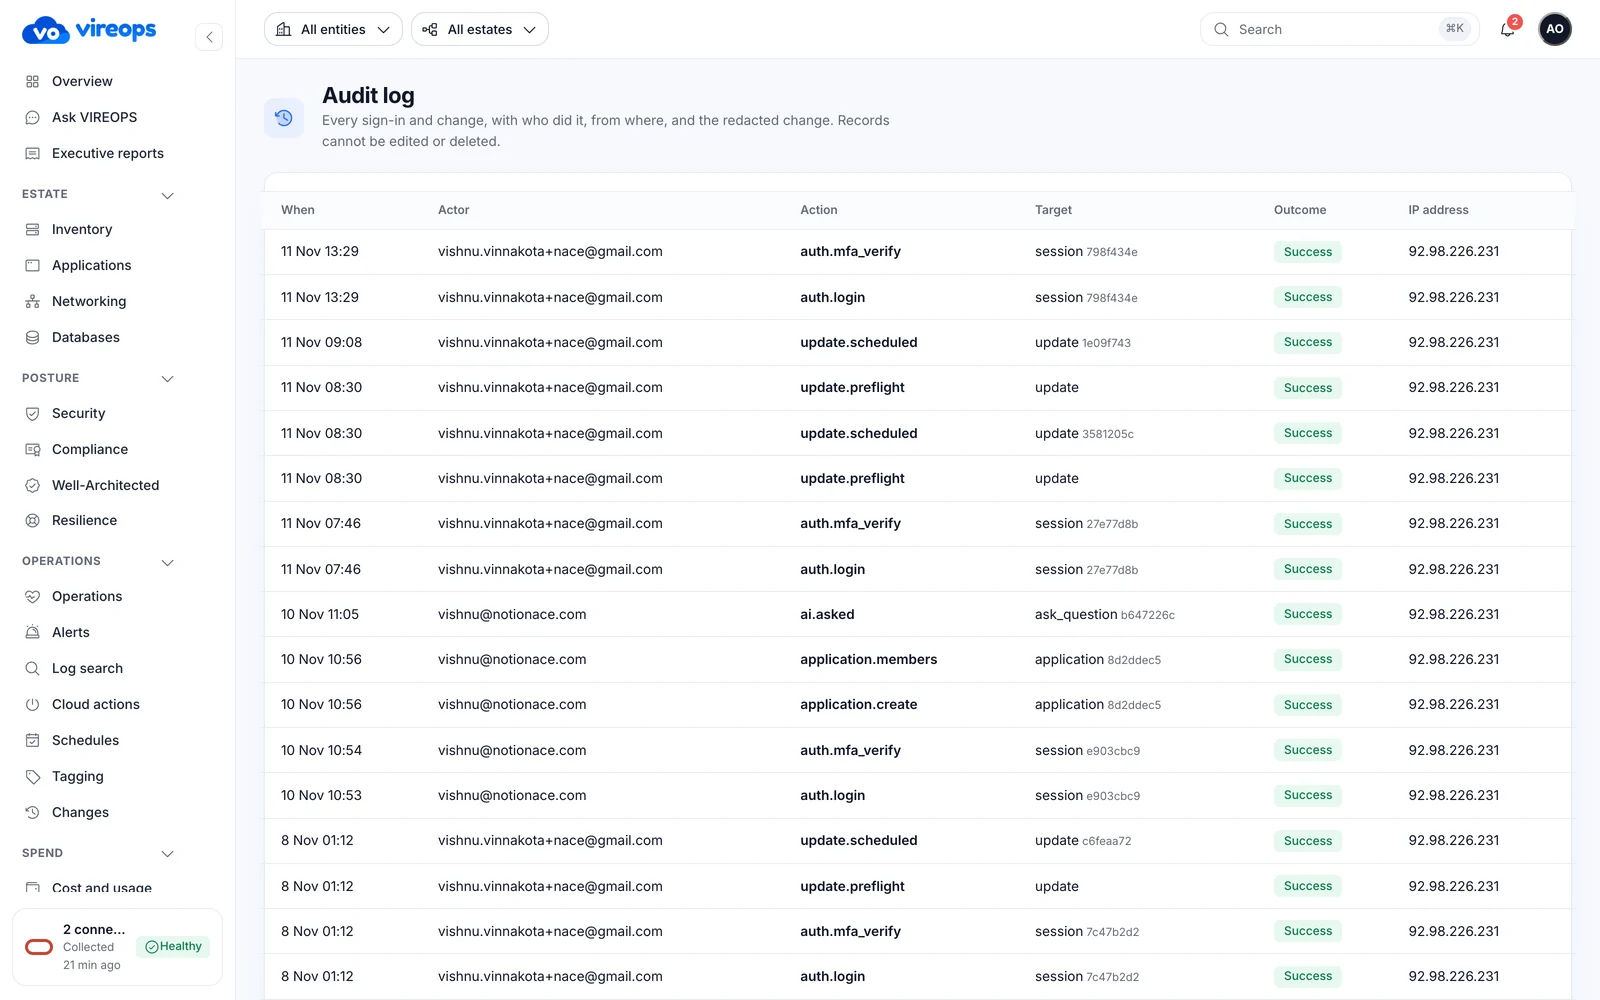
Every change, recorded in the same transaction
The audit log is append-only and written in the same transaction as the change it records, with redacted diffs and correlation IDs. Any change that isn't audited fails the tests.
- Cloud actions: who started it, who approved it, and every step
- Every log search, CMDB export and Ask VIREOPS question
- Metrics-export tokens created and revoked, support bundles downloaded
Signed, verifiable and never destructive
The licence is bound to the install's Ed25519 key and its host tenancy. Updates are signed releases you schedule into your own maintenance window.
Licence lease
- A signed lease renews every 24 hours, with 72 hours of offline grace, then restricted mode
- Data is never deleted, whatever the licence state
- Signed emergency grants of 24 or 72 hours cover Control Plane outages
- Replay, rollback and clock tampering are detected
Signed updates
- Signed release metadata with a hash chain, per-role AWS KMS keys, and protection against freeze, rollback and revocation
- Update Center: preflight (pass, warn or block), schedule, defer, install now, cancel and full step history
- Weekly maintenance windows. Deferral stops at release + 30 days (14 for security releases)
- Automatic recovery from the previous images and, when the schema changed, the pre-update backup
Restore-tested every night. Supported without a login.
Nightly backups
At 02:30, every dump is restore-tested into a scratch database and checked with a SHA-256. Seven are kept per kind, plus an extra backup before every update.
Off-site copy
Each backup is copied to the install's own Object Storage bucket, keeping the newest 14. Restore goes into a fresh database, and the replaced one is kept.
Scrubbed support bundles
You send a bundle with the ticket. Secrets are removed, and OCIDs, IPs, emails and names are replaced with placeholders. There is no vendor login.
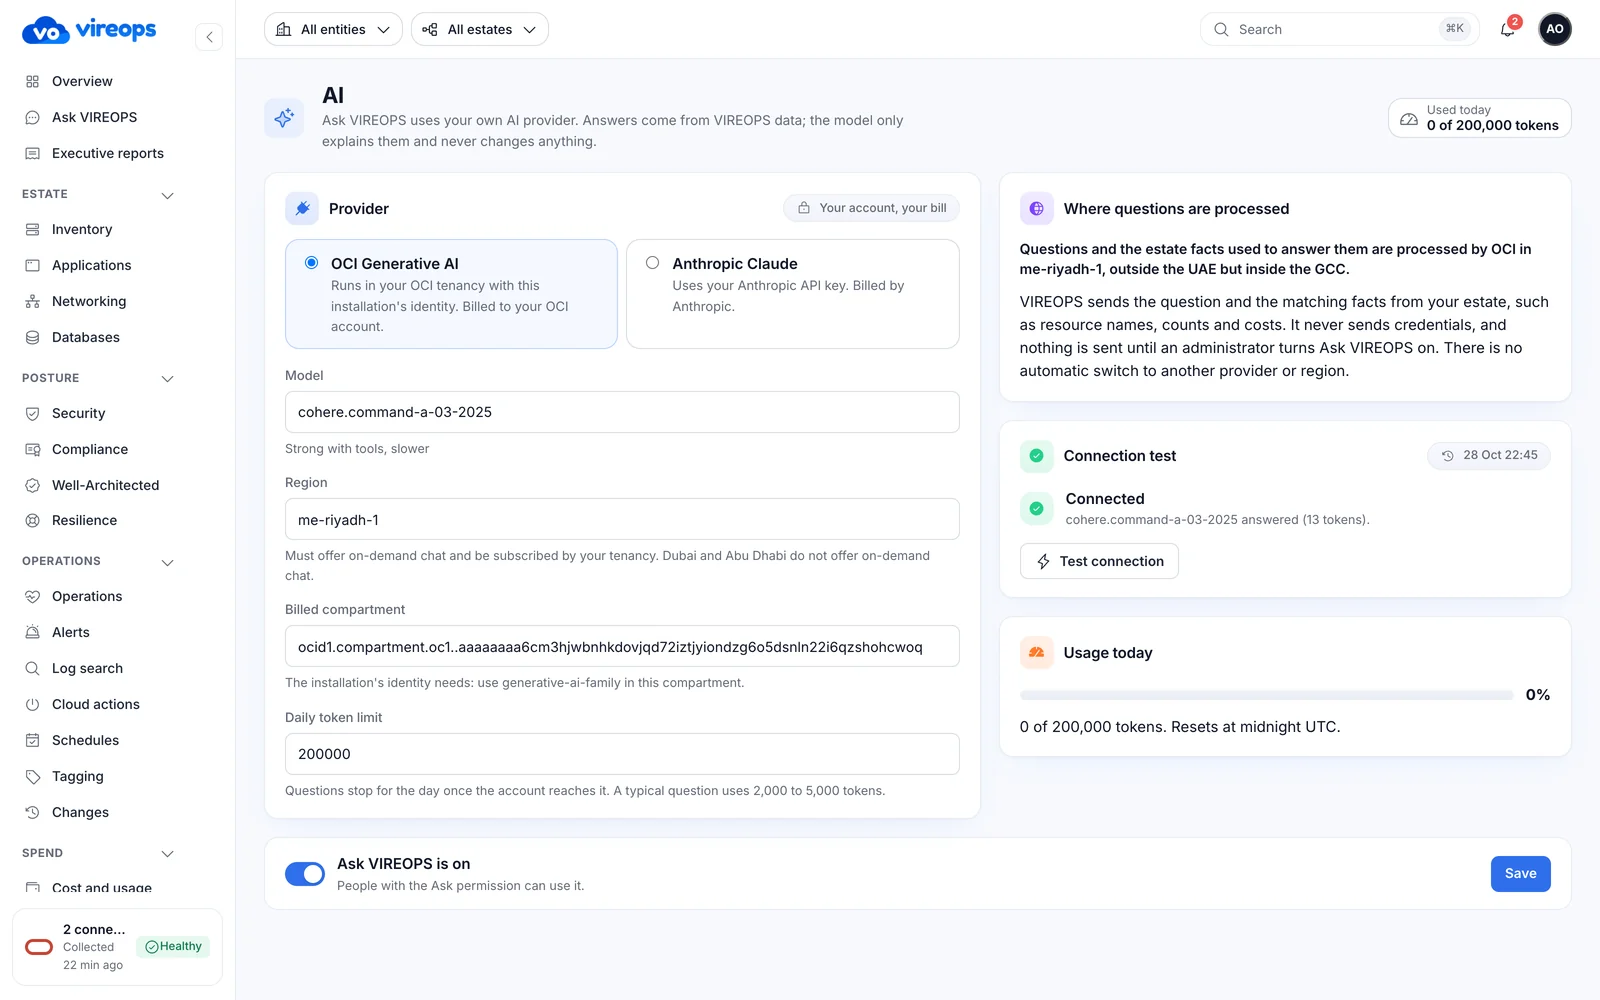
AI that explains, never decides
Ask VIREOPS is optional and off until an admin enables it. It runs on your own provider: OCI Generative AI in your chosen region, or your own Anthropic key.
- AI never computes scores or totals. Scores and rankings are fixed arithmetic
- No SQL, shell or cloud-write tools. Answers come from read-only tools that run in the asker's own permissions
- Every number in an answer must appear in the evidence, otherwise only the evidence is shown
- A daily token ceiling, and every question audited
- The product is complete with AI switched off, and CI enforces this
Built and supported by a certified team
VIREOPS is designed, built, deployed and supported by NotionAce, the same team that runs Oracle and AWS estates for enterprises.
Security questions
Can NotionAce log in to our install?
No. There is no vendor login. Support works from a scrubbed support bundle you choose to send, and fixes arrive as signed releases you install from the Update Center.
What happens if our install cannot reach NotionAce?
The lease renews every 24 hours. If renewal fails there are 72 hours of offline grace, then restricted mode. Signed emergency grants cover Control Plane outages. Your data is never deleted.
Can VIREOPS delete or terminate cloud resources?
No. Collection is read-only. Cloud actions need a separate opt-in OCI policy with each statement narrowed to one action, are started by a person, can require a second person's approval, and never delete, terminate or detach anything.
Where are AI questions processed?
By the provider you configure: OCI Generative AI in a region you pick, or your own Anthropic key. The residency disclosure is shown in Settings. Questions and answers are never sent to NotionAce.
Let's map your cloud estate together.
See VIREOPS on a live OCI estate: scored, priced and evidenced in one walkthrough. NotionAce deploys it in your tenancy within days.