Security and compliance you can evidence
Configuration checks mapped to SOC 2, ISO 27001 and CIS, plus regional frameworks, every control tied to evidence. Resilience and DR judged against the real resources, not a policy document.
One score, five dimensions, no guesswork
A dimension with nothing in scope shows "not assessed" and drops out of the weighting. Scores are arithmetic over fixed weights, never an AI judgement.
Customise it under Settings, Scoring: presets, weights, per-check switches and severity. Risk acceptances need a reason and an owner, last at most 365 days and can be revoked.
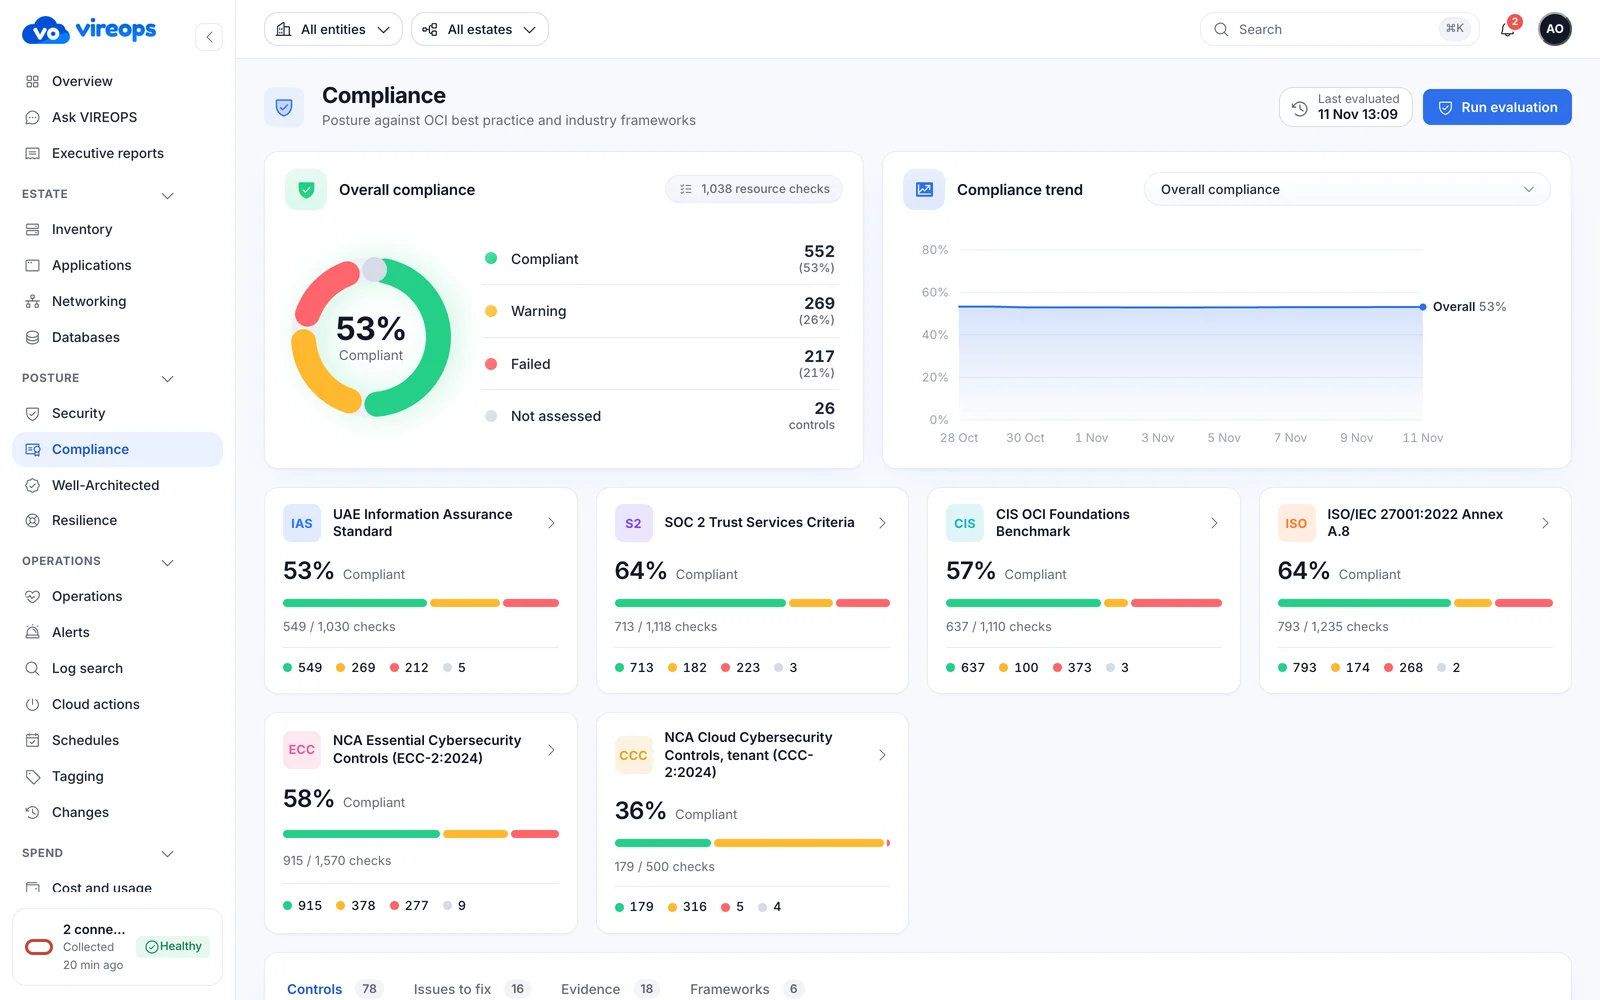
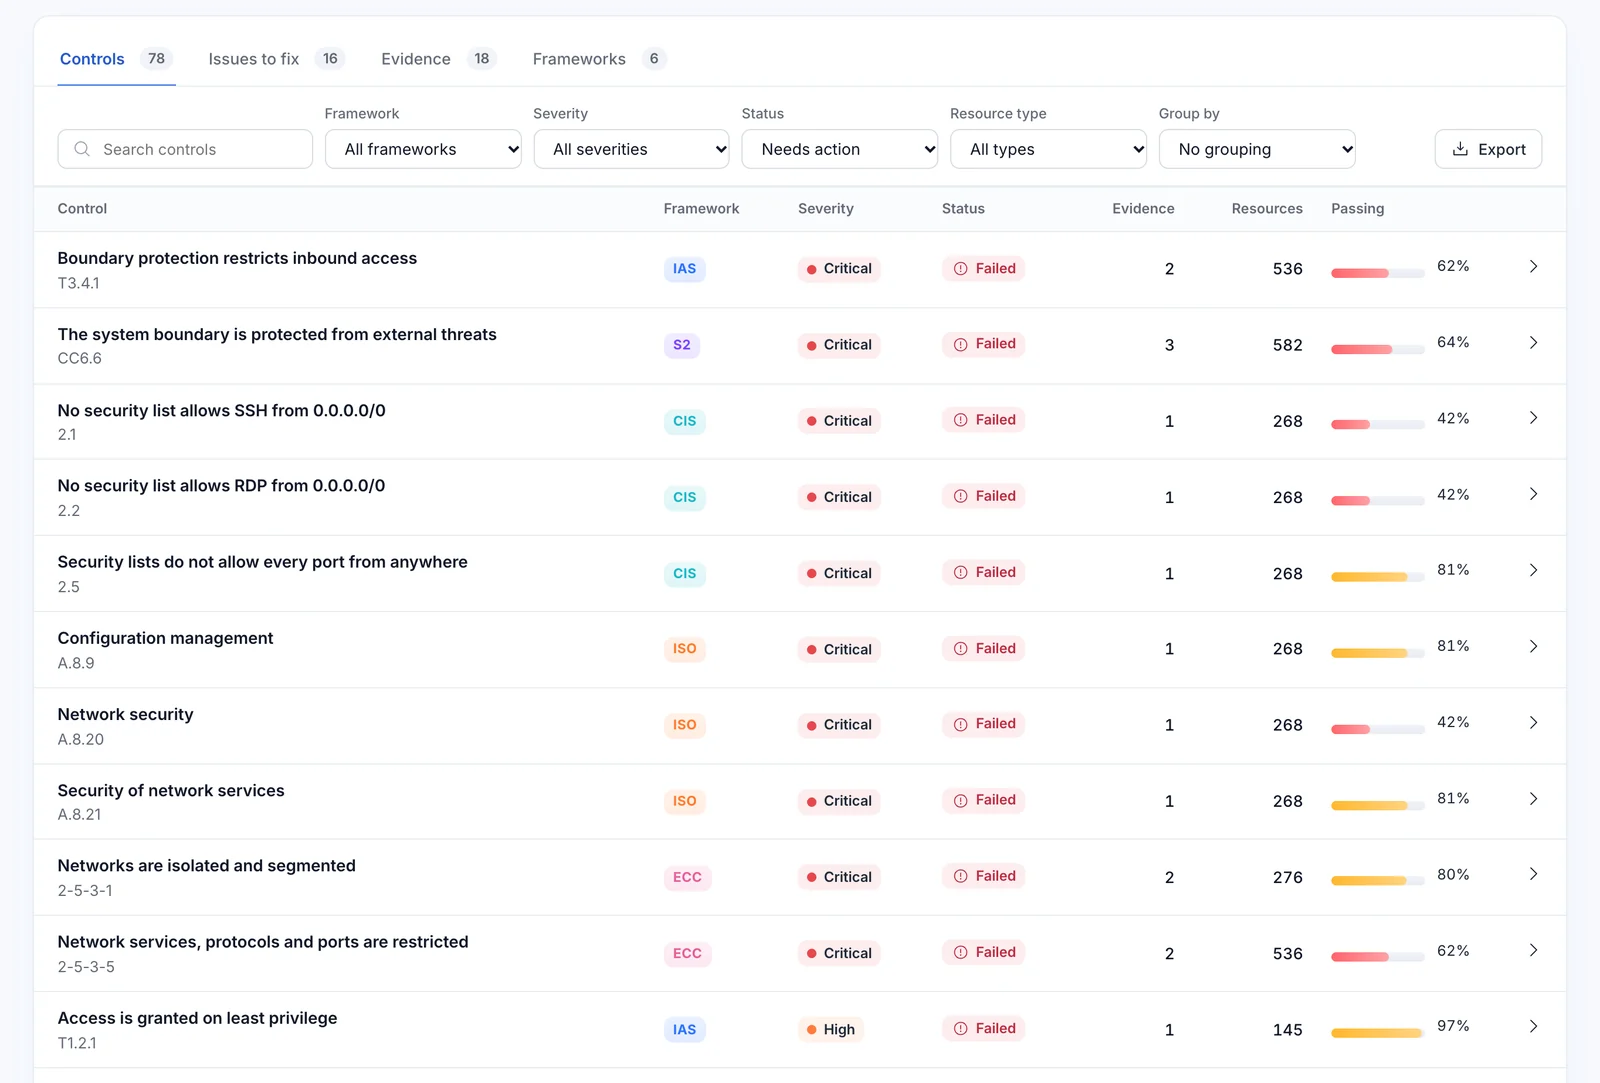
Would you pass a compliance audit tomorrow?
Each framework control maps to the configuration checks that evidence it, so the answer comes from what is actually deployed.
- No evidence, no pass. A control without evidence is "not assessed" and is never scored as passing
- NCA controls that configuration cannot evidence are listed as organisational, never scored as passing
- Controls open on "Needs action" and group by severity, framework or status
- A Compliance framework report lists every control with its status and evidence, for auditors
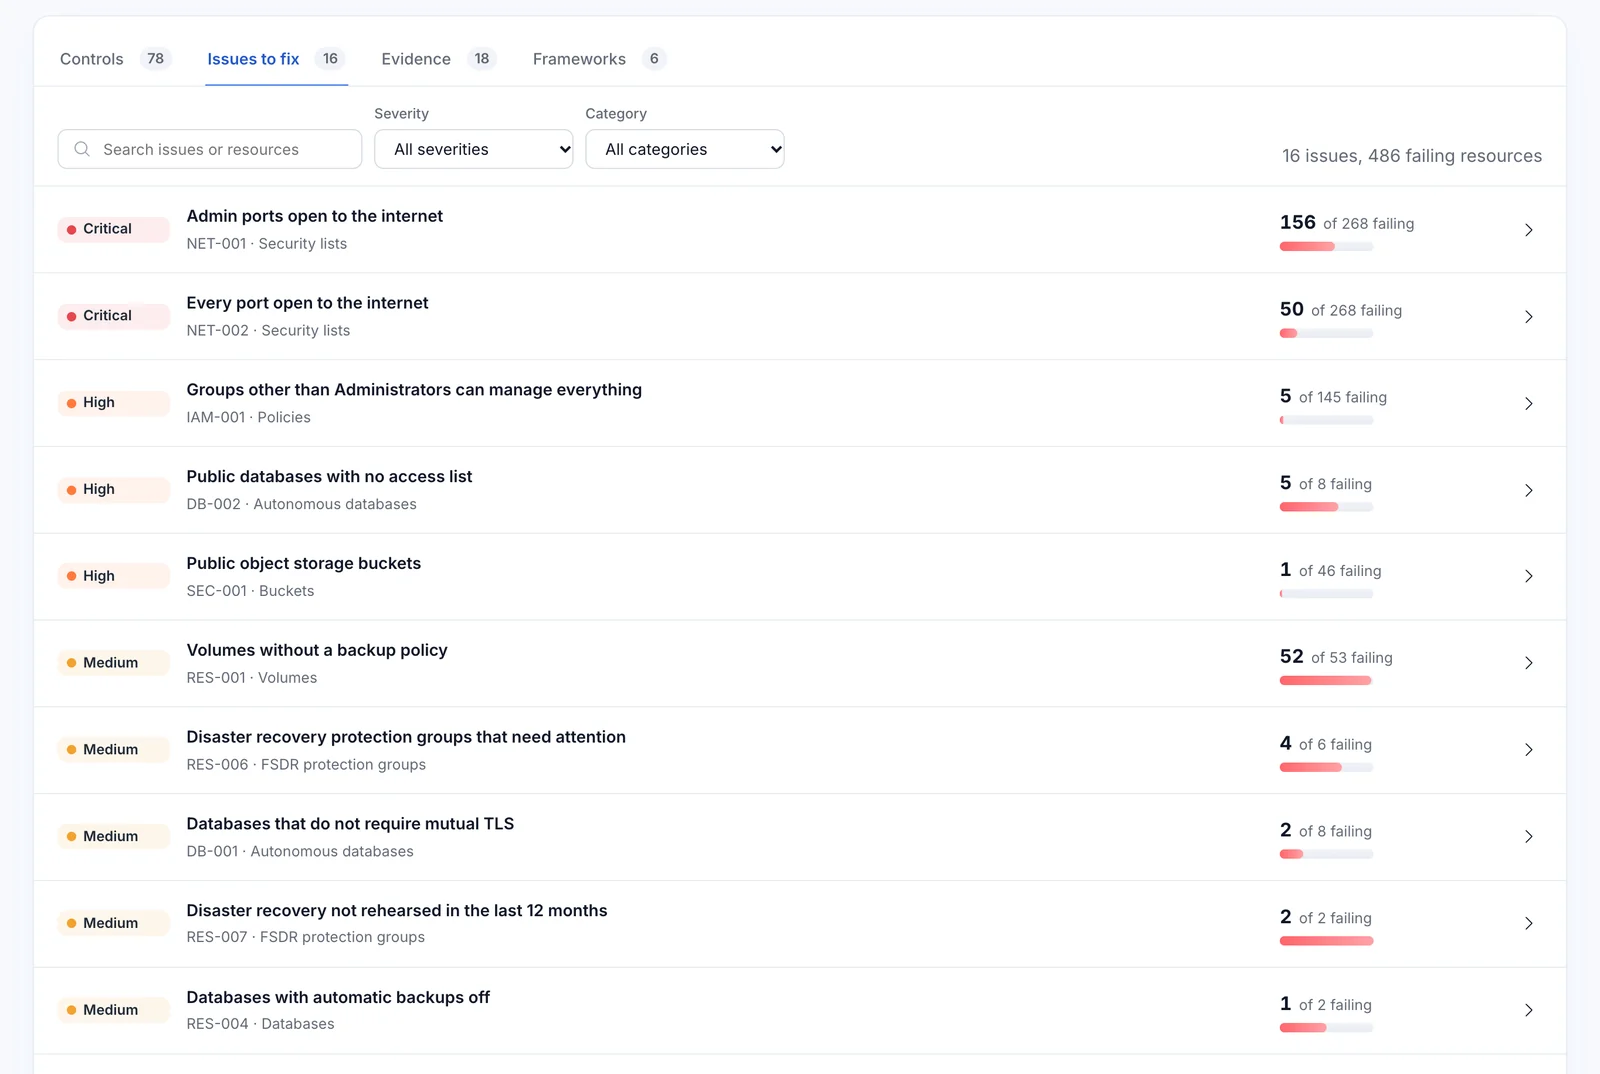
Worst first, with how to fix it
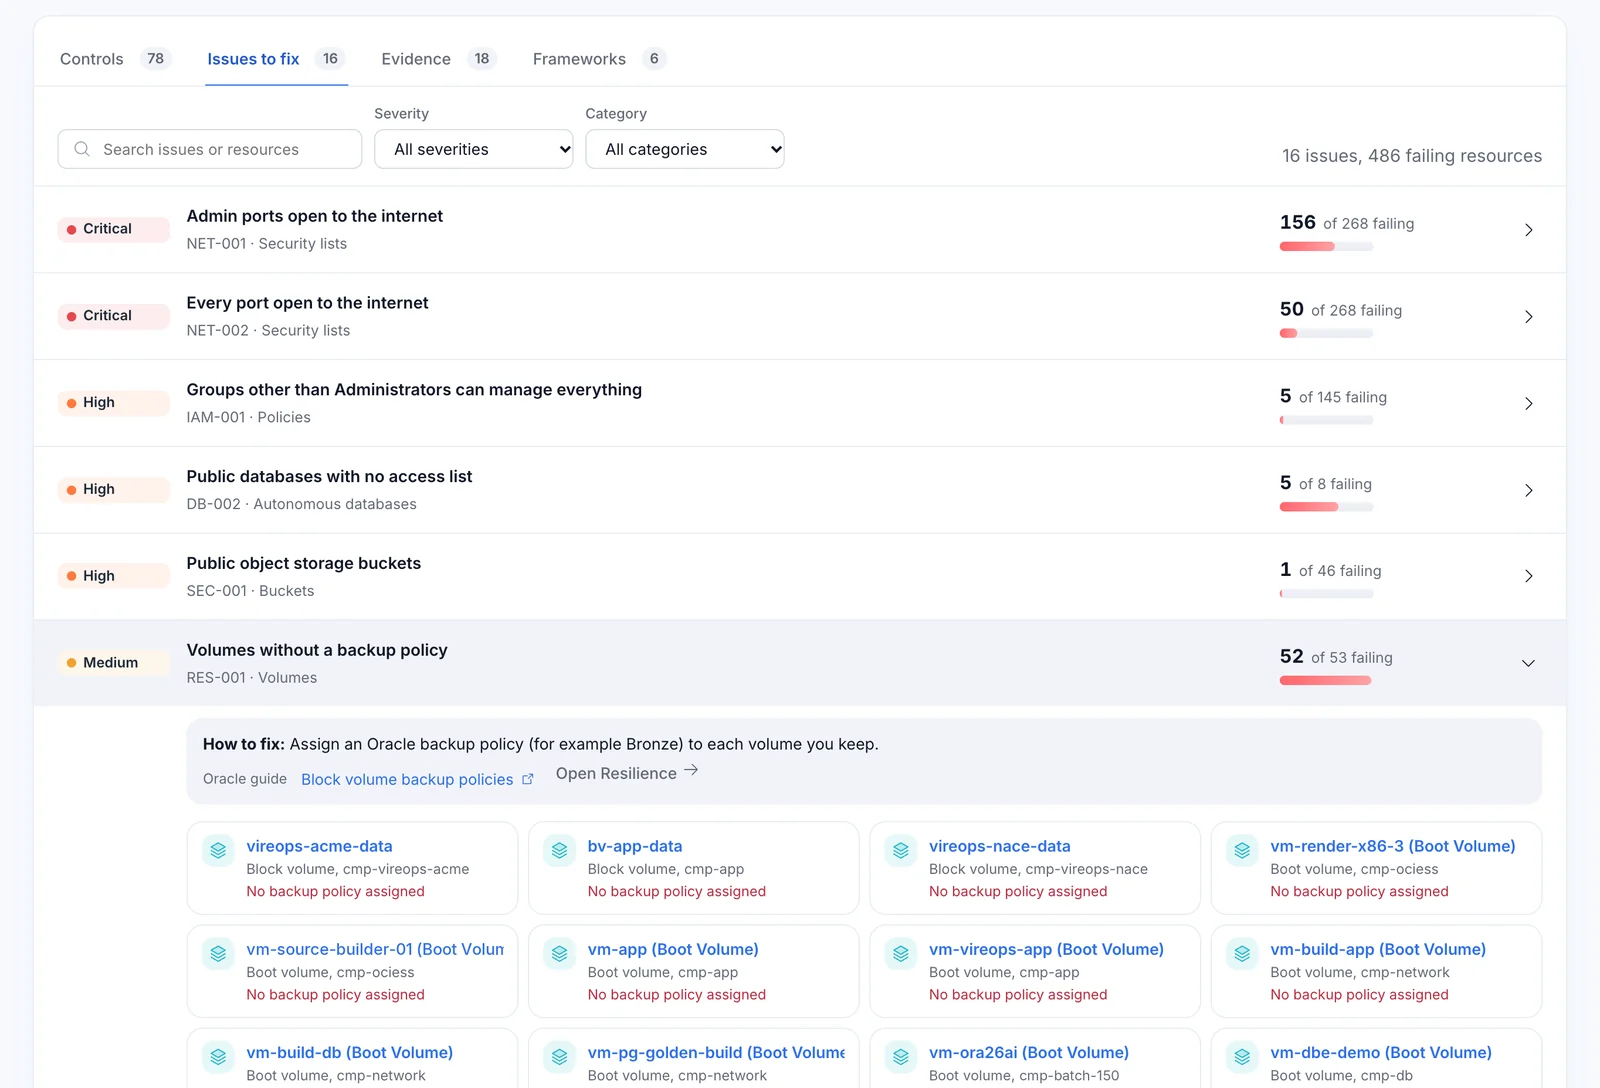
Failing resources are grouped by check, worst first. Each check carries how to fix it, Oracle's own guide and links to the affected resources.
- Security, Resilience and Overview link straight to the matching issue
- Shared checks also judge AWS security groups, S3 bucket policies and RDS settings; OCI-only checks never judge AWS resources
Which servers are exposed and unpatched?
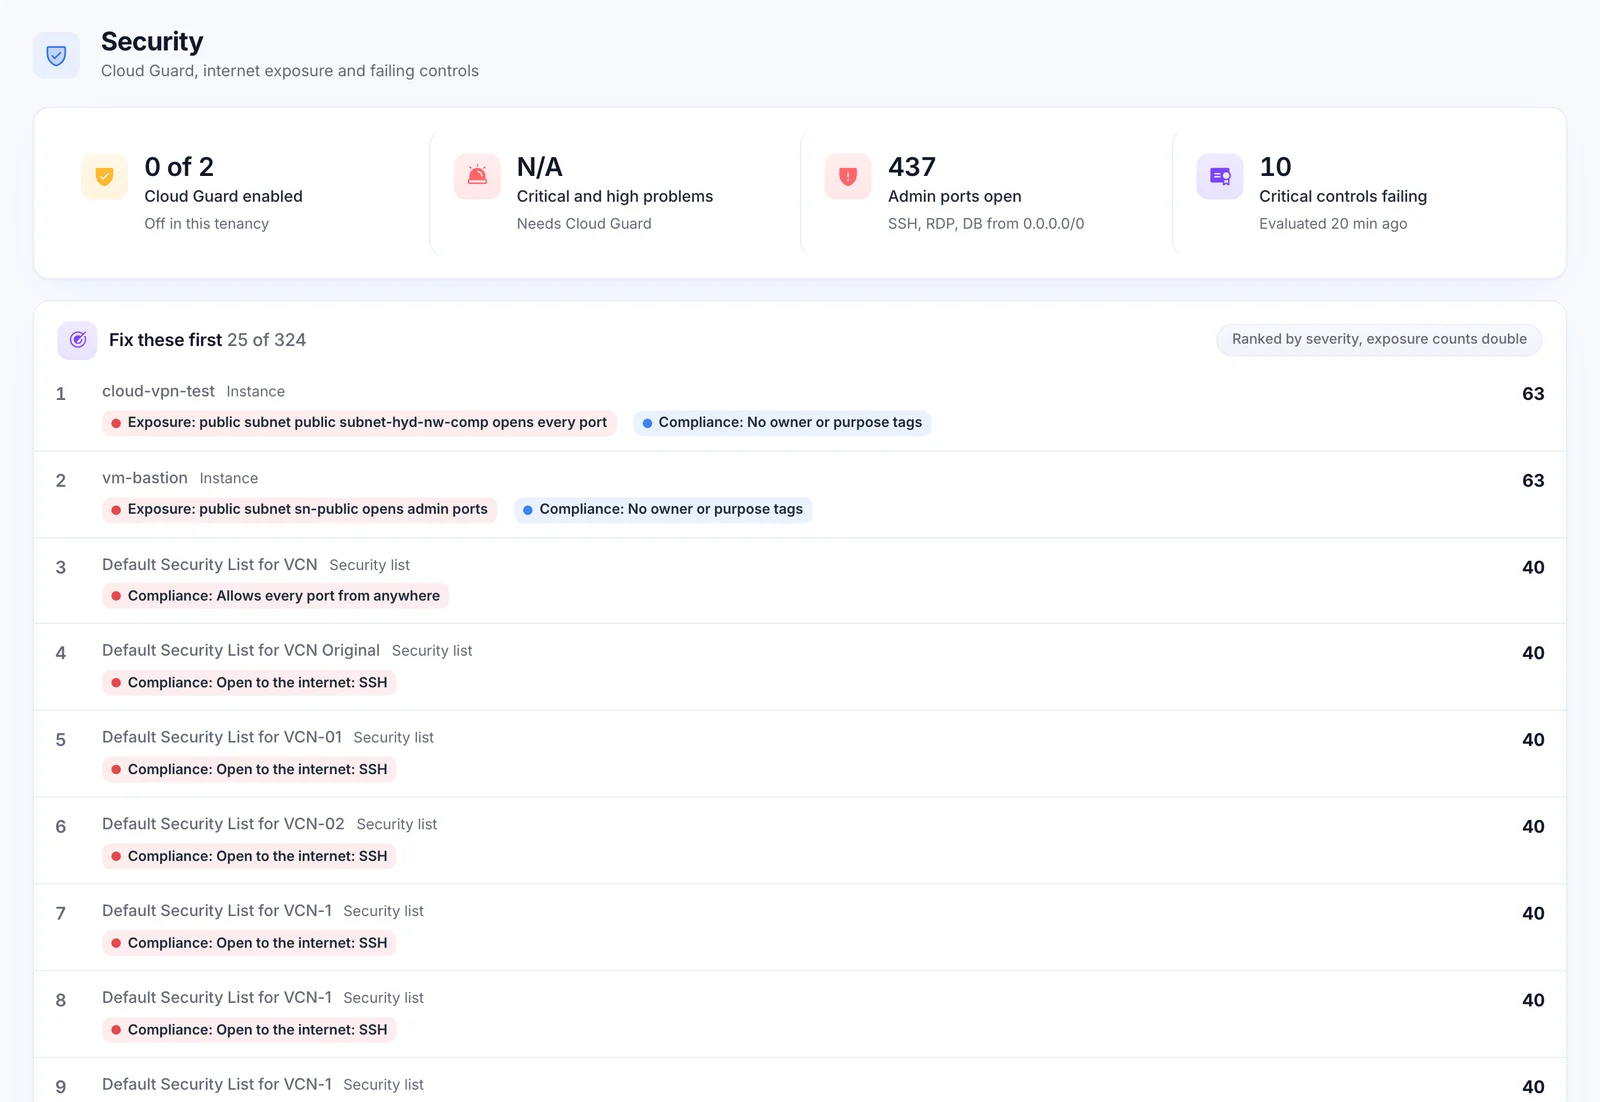
The Security page ranks the top 25 resources from failing checks, Cloud Guard problems, vulnerabilities and firing alerts, using fixed weights. An instance reachable from the internet that is also vulnerable counts double.
- Cloud Guard state per connection and open problems by risk
- Internet exposure tiles that open the matching compliance issue
- Failing critical and high controls, each opening its framework
- Arithmetic only, never an AI score. The Overview shows the top 5
Open CVEs and the hosts they affect
From OCI Vulnerability Scanning: instances by worst finding, scan coverage, and open CVEs with the hosts affected. It goes live on an install once the read vss-family grant is added.
- A tenancy with no scan targets says so. It never reports "no vulnerabilities"
- AWS Inspector vulnerabilities and Security Hub findings through the AWS connector
- Patch from VIREOPS through OS Management Hub, with approval and audit
If a region fails, what recovers?
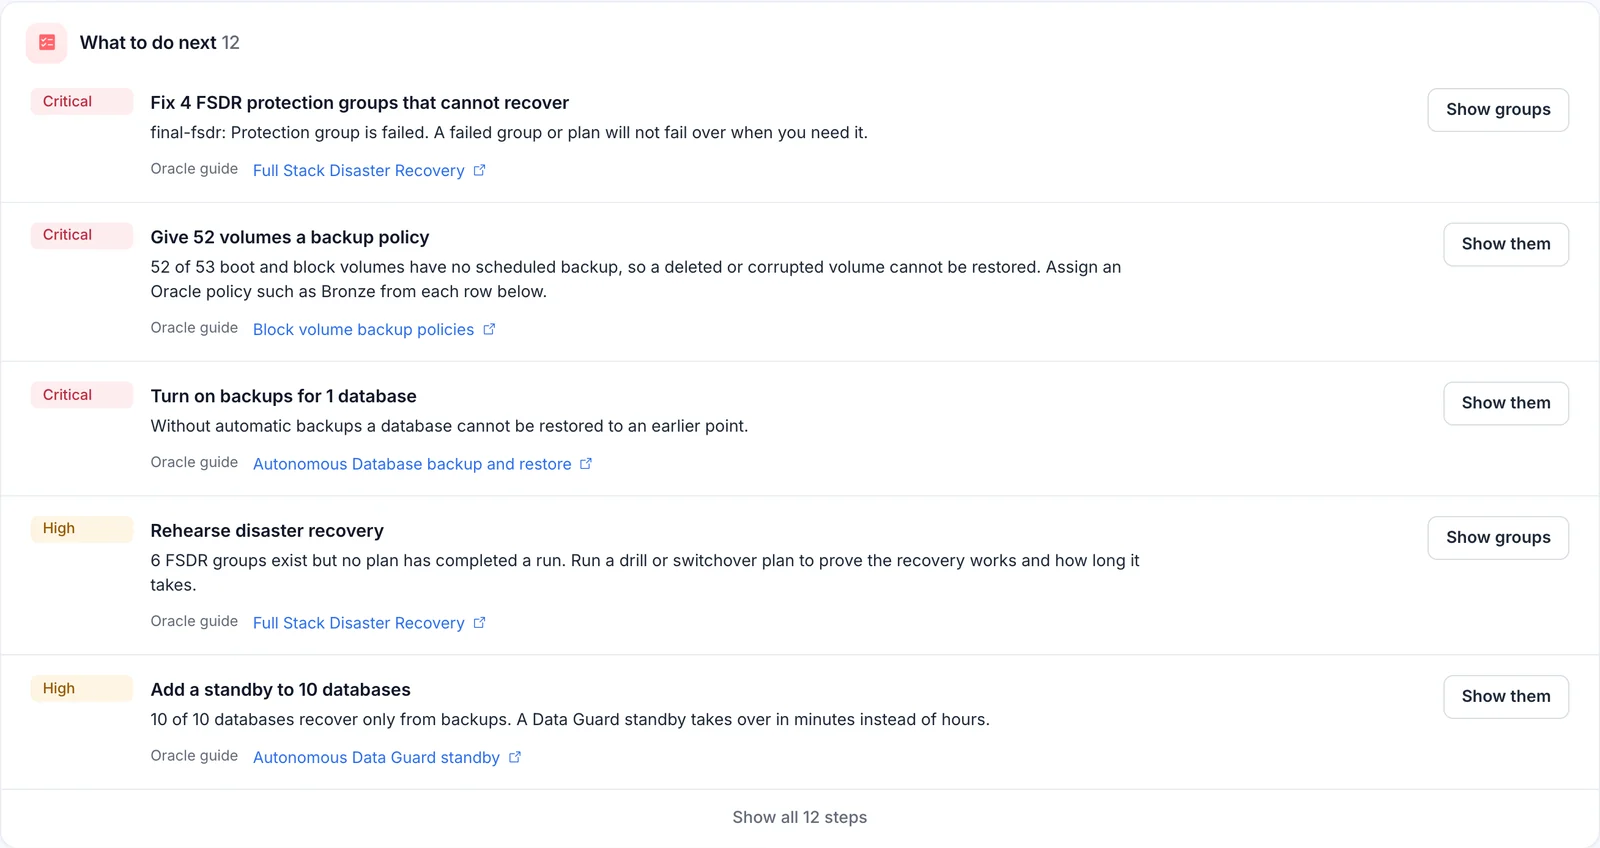
Set DR targets per application (tier, RPO, RTO and DR region) and VIREOPS judges them against the actual resources: backups, standbys, Data Guard, Full Stack DR groups and cross-region copies.
- Full Stack DR coverage and its last rehearsal
- Protection-coverage tiles, and "Enable backups" on unprotected volumes
- What to do next: ranked directions, each with "Show them", Oracle's guide and the screen to act on
38 practices across Oracle's five pillars
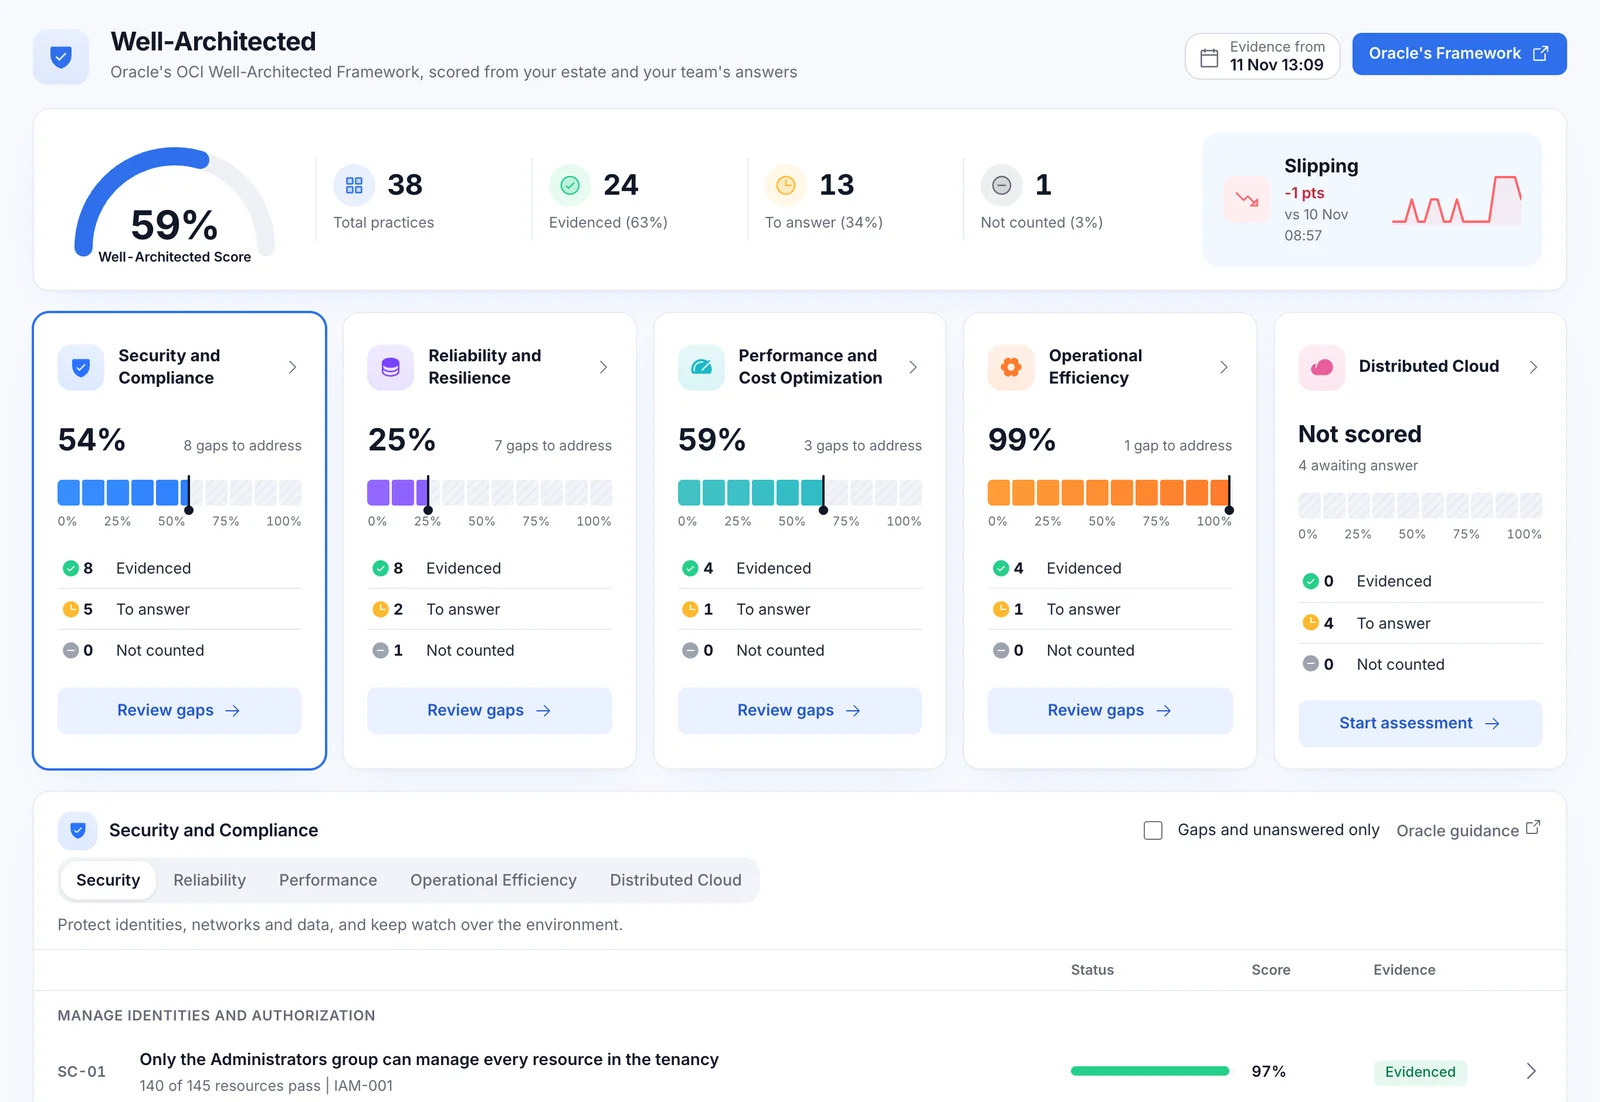
Each practice is evidenced by checks, by estate signals or by a person's answer, with a trend from stored snapshots. The review is kept separate from the Estate Score.
- Security and compliance, reliability and resilience, performance and cost, operational efficiency, distributed cloud
- 12 ranked next steps, each linked to Oracle's guide
What Secure evaluates
Every finding points to the resource and the evidence that produced it.
| Capability | Detail | Status |
|---|---|---|
| Compliance frameworks | SOC 2, ISO 27001 A.8, CIS OCI, plus regional: UAE IA, NCA ECC-2:2024, NCA CCC-2:2024 tenant controls | Live |
| Cloud Guard | Status per connection and open problems by risk | Live |
| Fix these first | Top 25 on Security, top 5 on Overview; fixed weights, exposed and vulnerable counts double | Live |
| Vulnerability Scanning | Worst finding per instance, scan coverage, open CVEs with hosts affected | Built |
| Resilience and DR | Per-application RPO/RTO, Full Stack DR groups, plans and runs, DB backups and Data Guard, volume groups, backup policies | Live |
| Well-Architected | 38 practices, 5 pillars, trend from snapshots | Live |
| Risk acceptance | Reason, owner, up to 365 days, revocable and audited | Live |
| AWS checks | Security groups, S3 bucket policies, RDS public access and backups in the shared checks | Built |
| CIS AWS, AWS resilience | Planned for Release 2 | Not yet |
| NCA CCC data classification levels | Planned | Not yet |
Questions about Secure
Does VIREOPS replace an external audit?
No. It gives you continuous, evidenced answers for the technical controls that configuration can prove, and lists the organisational controls it cannot evidence so your auditors see the full picture.
How is "not assessed" different from "passing"?
A control passes only when evidence shows it passing. If nothing in scope evidences it, it shows "not assessed" and never counts as a pass. Missing data is never "all clear".
Is the Estate Score calculated by AI?
No. Scores, totals and rankings are deterministic arithmetic with fixed weights you can review and adjust. AI never computes scores or totals.
Which grants does Secure need?
Read-only access from the least-privilege policy the connection wizard generates. Vulnerabilities need the read vss-family grant and network-access answers need a narrow NSG-rules grant.
Can I accept a risk instead of fixing it?
Yes. A risk acceptance needs a reason and an owner, lasts at most 365 days, can be revoked and is audited.
Let's map your cloud estate together.
See VIREOPS on a live OCI estate: scored, priced and evidenced in one walkthrough. NotionAce deploys it in your tenancy within days.